A human-in-the-loop AI approval workflow lets an AI system prepare work, recommend an action, or execute low-risk steps while a qualified person reviews the actions that could create real business impact. For US teams, this pattern is often the practical bridge between an impressive agent demo and a production workflow that customers, operators, and compliance stakeholders can trust.
The short answer is simple: do not ask a human to approve everything, and do not let an agent decide by itself which actions deserve review. Classify actions by impact and reversibility, enforce approval in application logic, show the reviewer the evidence behind the recommendation, and write the decision to an audit trail. That structure keeps routine work moving while preserving accountability for sensitive actions.
When an approval gate is necessary
Approval belongs before an action that is expensive, externally visible, difficult to reverse, regulated, or likely to affect a person or customer. Examples include sending a contract or customer email, changing account permissions, issuing a refund, approving a vendor, exporting sensitive data, publishing content, or changing a production configuration. A generated summary or an internal classification may not need the same gate when the source records remain available and the result is easy to correct.
Use three questions to decide whether a step needs review. What can happen if the output is wrong? Can the action be reversed without cost or customer harm? Who has the authority to accept that risk? The answers create a decision policy that is easier to test than a vague instruction such as “ask a human when uncertain.”
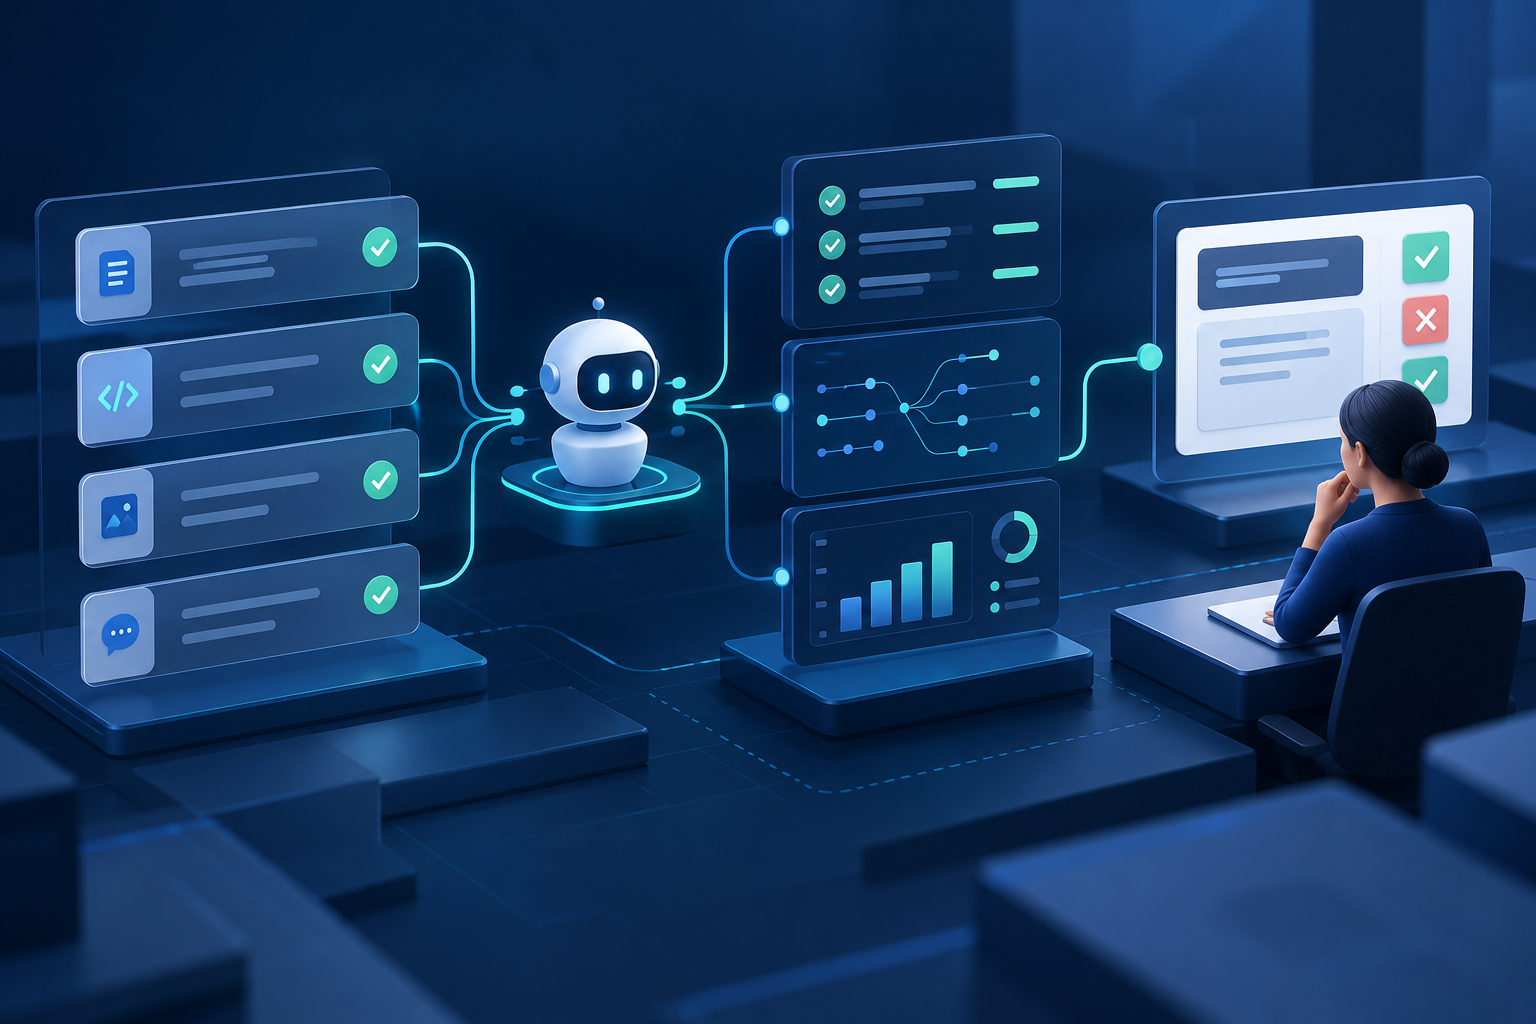
A six-stage approval workflow
- Intake: Capture the requester, account, requested action, deadline, source documents, and data sensitivity.
- AI preparation: Extract fields, summarize evidence, compare the request with policy, and draft the proposed action.
- Risk classification: Combine deterministic rules with signals such as amount, external visibility, confidence, missing evidence, and permission scope.
- Reviewer routing: Send the task to the person who owns the decision, with a backup and a response deadline.
- Decision: Support approve, reject, request changes, escalate, and return-for-information as explicit states.
- Execution and evidence: Execute only the approved payload, then store the decision, actor, timestamp, result, and exceptions.
This state model prevents the most common failure in agent workflows: a user clicks a button, but the system cannot show what was approved or whether the payload changed afterward. The approval record should reference a versioned proposal or a hash of the exact fields that will be sent to the downstream system.
Design the reviewer experience
A reviewer should not need to open five tabs and reconstruct the agent’s reasoning. Present the original request, source links, extracted fields, policy checks, uncertainty flags, proposed action, downstream effects, and a clear alternative. Make edits visible. If a reviewer changes a subject line, amount, recipient, or permission scope, save both the proposed and approved values so the team can learn from the difference.
Keep the queue small by routing only actions that cross a policy threshold. A queue full of low-value approvals trains people to rubber-stamp. For low-risk work, use asynchronous review or sample-based quality checks. For high-risk work, require named approvers, dual control, or a second review when the business process warrants it.
Enforce the gate in code, not in a prompt
A prompt can describe a policy, but it cannot reliably enforce authorization. The application must authenticate the user, check tenant and record permissions, validate typed inputs, and refuse execution when the workflow state is not approved. Separate read tools from write tools. Use idempotency keys so a retry cannot send a duplicate message or create a second ticket. Expire stale approvals when the record, amount, recipient, or policy version changes.
Log enough evidence to investigate a failure without copying unnecessary personal data. Record the workflow ID, actor, tool, record identifier, policy result, model version, approval state, execution result, and a link to the source. Review the NIST AI Risk Management Framework for a broader risk vocabulary, then adapt it to the decisions your business actually makes.
Roll out in shadow mode first
Start with a two-stage rollout. In shadow mode, the AI prepares recommendations but a person completes the existing process. Compare the recommendation with the human result, measure missing evidence and false escalations, and turn real exceptions into regression cases. In assisted mode, the reviewer can approve a validated action from one screen. Only after the team has evidence should the workflow execute low-risk actions automatically.
Define operating metrics before launch. Useful measures include approval turnaround time, escalation rate, reviewer edits, unauthorized actions blocked, duplicate actions prevented, task completion, cost per completed task, and the rate of post-approval corrections. These metrics tell you whether the workflow is safer and faster, not merely whether the model produces fluent text.
How DeepVention Labs can help
DeepVention Labs helps US teams turn agent ideas into controlled products through AI workflow automation, integration architecture, evaluation, and observability. Our AI governance guide provides a companion checklist for ownership, data boundaries, and policy review. The goal is a workflow where people remain accountable for consequential decisions while automation handles the repeatable preparation around them.
Common approval design failures
The first failure is an approval request with no context. A reviewer sees a polished recommendation but cannot inspect the source or understand what will happen next. The second is a gate that exists only in the user interface. If an API, retry worker, or alternate integration can bypass it, the control is not real. The third is a queue that measures clicks instead of decisions. A fast approval may simply mean the reviewer could not see enough to challenge the proposal.
Prevent these failures with a written policy matrix. For each action, record the risk tier, required evidence, eligible approver, expiration period, and recovery path. Review the matrix quarterly and after an incident. If an action becomes more consequential, move it to a stricter tier rather than quietly adding another prompt. This makes the workflow understandable to engineering, operations, security, and the people who ultimately own the outcome.
Meaningful oversight is a product capability, not a ceremonial step. Give reviewers enough evidence to make a decision, give them a way to edit or reject the proposal, and give the business a durable record of what happened. That is how a human-in-the-loop workflow improves speed and accountability at the same time.
Build an LLM GTM system around this topic.
Explore strategy, GEO content, proof architecture, distribution, automation, and visibility measurement.