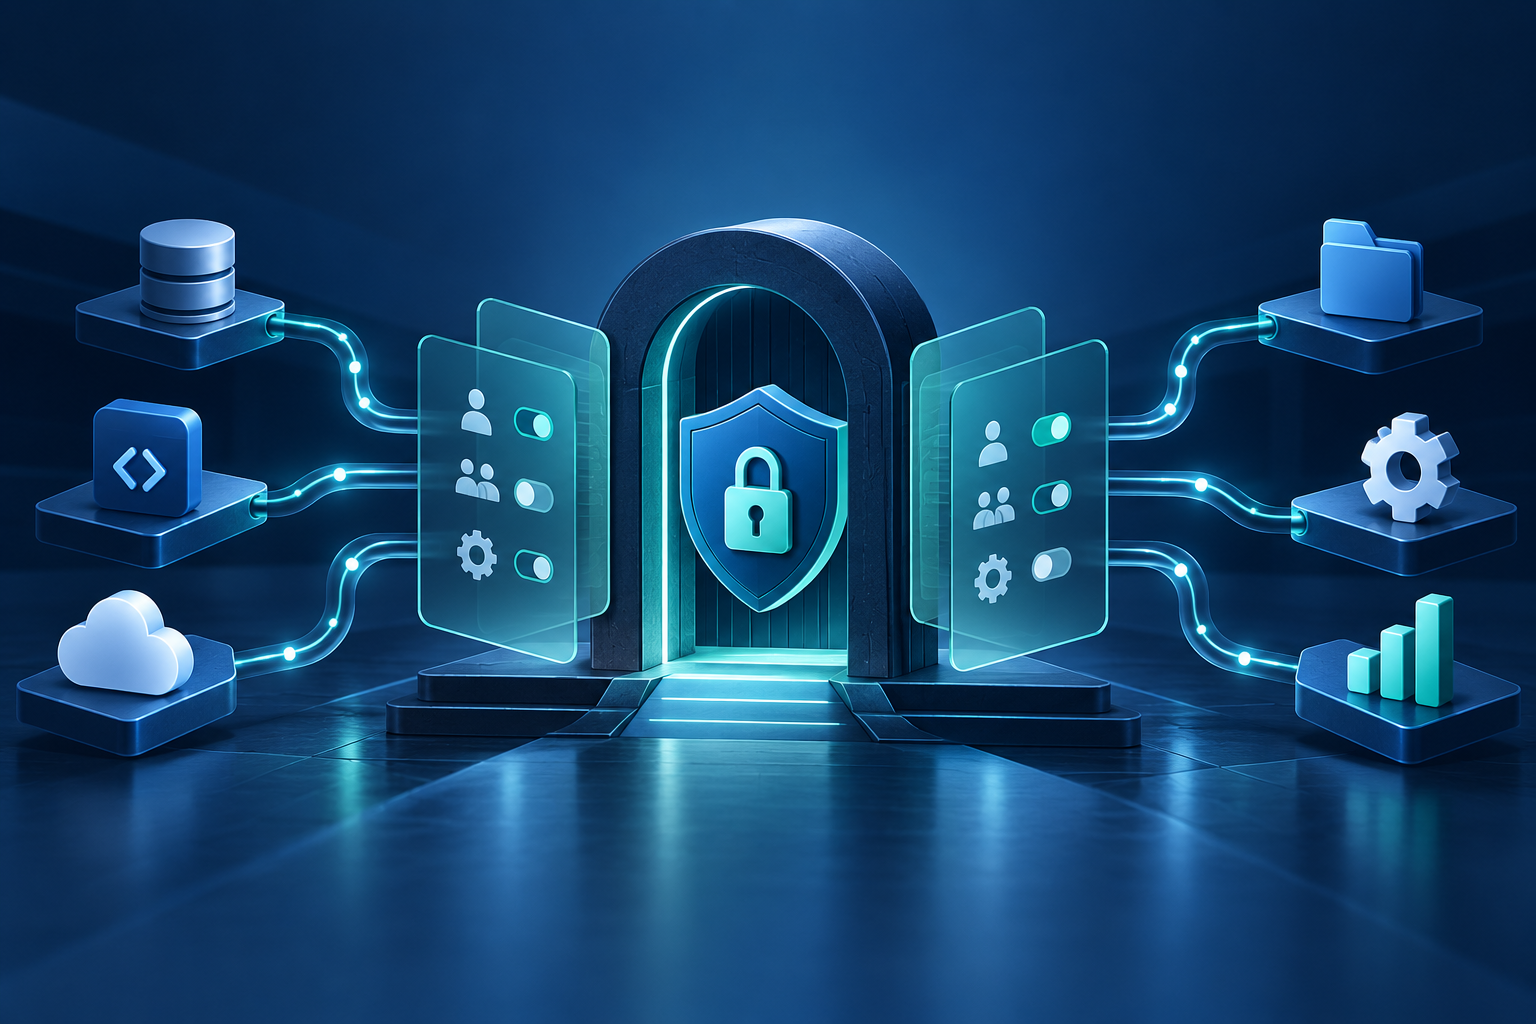
MCP security starts at the integration boundary, not in the model prompt. A production Model Context Protocol (MCP) deployment should authenticate every caller, expose only approved tools, validate typed inputs, isolate tenant data, and record enough evidence to investigate each run. The protocol can standardize how context and tools are exposed, but the host application remains responsible for authorization and operational safety.
What does MCP security need to protect?
An MCP host may connect a model to files, databases, APIs, or business actions. That creates more than a prompt-injection concern. The system must protect identities, secrets, customer records, tool arguments, durable state, and the downstream services that receive requests. The OWASP MCP Security Cheat Sheet is a useful primary reference for threat modeling the protocol boundary.
How should tools and permissions be scoped?
- Give each user, tenant, and service identity only the tools required for its workflow.
- Separate read operations from actions that change durable data.
- Use explicit allowlists for servers, tools, resources, and outbound destinations.
- Re-check authorization at execution time instead of trusting a model-generated instruction.
- Use short-lived credentials where the connected system supports them.
What validation belongs before a tool call?
Validate the tool name, argument types, record scope, requested fields, and expected side effects before execution. Reject unknown fields and unexpected destinations. Add idempotency keys to retriable writes so a timeout cannot create duplicate tickets, messages, or payments. Treat retrieved text as untrusted data and keep it separate from the instructions that define the workflow.
Which logs and tests make MCP safer?
Capture the authenticated actor, selected tool, policy decision, validation result, target system, outcome, and approval state while minimizing sensitive payloads. Test prompt injection, confused-deputy behavior, cross-tenant access, malformed arguments, replayed requests, unavailable tools, and partial failures. Microsoft also recommends explicit permission boundaries and input validation in its MCP security guidance.
When is an MCP integration ready for production?
A release should have a named owner, a documented data boundary, tested authorization, representative security cases, useful traces, a disable path, and a human escalation route for consequential actions. DeepVention Labs helps teams design secure MCP infrastructure around production systems without treating the model as the security boundary.
Build an LLM GTM system around this topic.
Explore strategy, GEO content, proof architecture, distribution, automation, and visibility measurement.